Kernel Syscall Surface Exposure as the Core Argument Against Container Isolation for AI Agents
Shared host kernels are the real risk; per-agent microVMs fix it.
Soren Valck
Section
12 stories in Micro-VM Infrastructure.
Shared host kernels are the real risk; per-agent microVMs fix it.
Hardware isolation is the easy part; running the fleet is the cost.
Firecracker platforms differ on five dimensions, from egress to snapshots.
Firecracker gives AI agents isolated kernels to safely execute untrusted generated code.
Micro-VMs offer hardware-enforced isolation that containers and serverless simply cannot provide.
Firecracker isolates agent code execution with its own kernel and network controls.
OverlayFS layers provide reversible filesystem state and storage efficiency for untrusted AI agents.
Per-VM networking isolates agents and tracks their actions across fleet scale.
Choosing the right kernel and stripping unnecessary features cuts boot time and isolation risk.
Firecracker micro-VMs on bare metal enable agent fleets to pause idle work and resume it instantly.
Firecracker isolates AI agent code with its own kernel and boots in milliseconds.
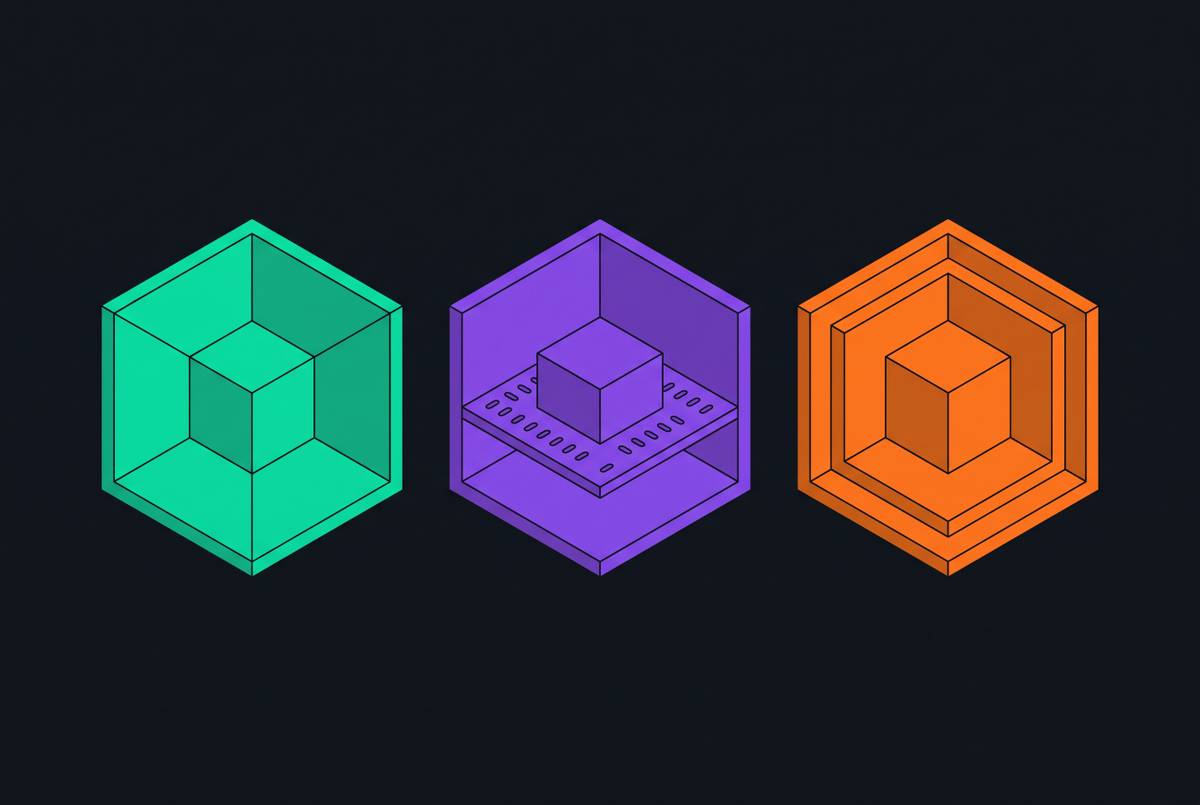
Compares how three sandbox runtimes handle syscalls from untrusted agent code.